This article is intended to assist Customer Experience Engineers, Network Engineers, Field Engineers, with complete port requirements for firewall configuration and network planning for the Crosswork Assurance platform. Use this guide when configuring firewalls, security groups, or troubleshooting connectivity issues. Getting ports wrong is one of the most common causes of installation failures and connectivity problems.
Network Topology Diagram
This diagram shows the network architecture and how different components communicate. Use it to understand which ports need to be open between which components:
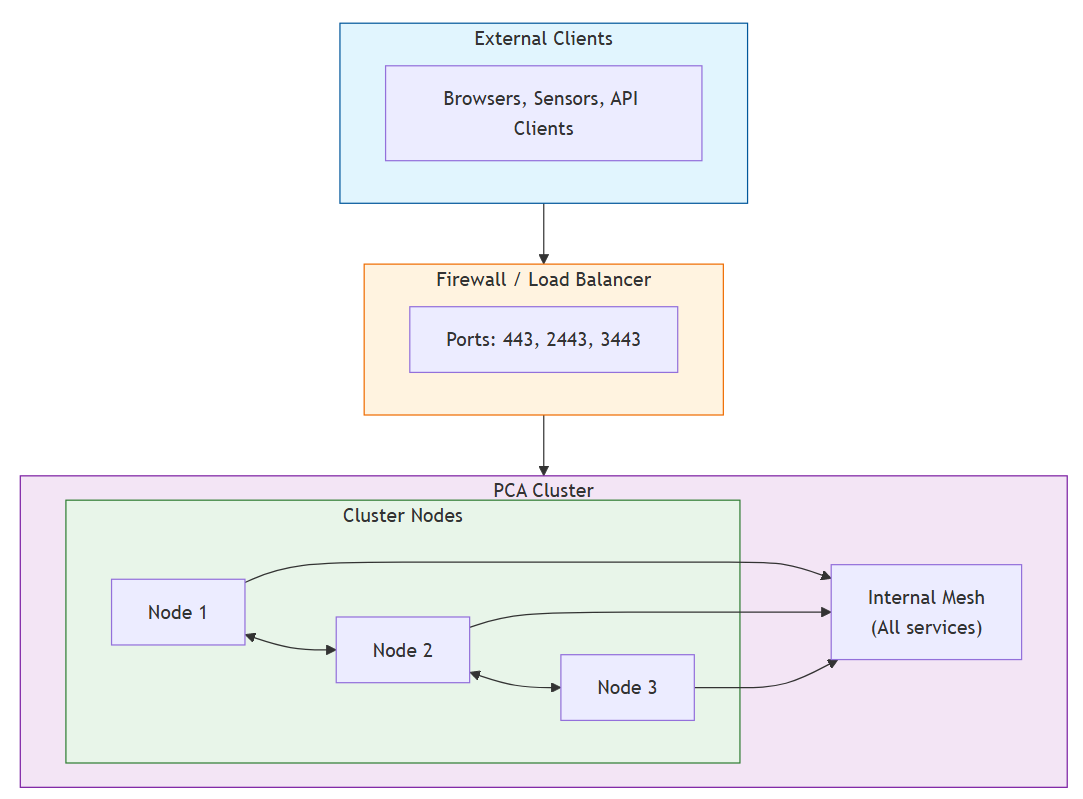
Quick Reference
If you need a quick overview, this table summarizes the port categories. Detailed tables follow for each category:
| Category | Ports | Direction |
|---|---|---|
| External Access | 443, 2443, 3443, 4443, 30000 | Inbound |
| Inter-Node | 2380, 4789, 6443, 9091, 9443, 10249-10256 | Bidirectional |
| Local Processes | 2380, 4789, 6443, 9091, 9443, 10249, 10250, 10256 | Local only |
External Access Ports
These ports must be accessible from outside the cluster for user and administrative access. The specific ports depend on whether you're using DNS mode or No-DNS mode.
DNS Mode (Recommended)
In DNS mode, all applications share port 443 and are differentiated by hostname. This is the recommended configuration for production deployments:
| Port | Protocol | Application | Description |
|---|---|---|---|
| 443 | TCP | Tenant UI | Main application access (https://{domain}) |
| 443 | TCP | Deployment UI | Deployment dashboard (https://deploy.{domain}) |
| 443 | TCP | Zitadel (auth) | Identity management (https://auth.{domain}) |
| 443 | TCP | Grafana | Metrics dashboards (https://grafana.{domain}) |
Note: In DNS mode, all applications share port 443 and are differentiated by hostname.
No-DNS Mode
In No-DNS mode, each application uses a different port. Use this when you can't configure DNS records:
| Port | Protocol | Application | Access URL |
|---|---|---|---|
| 443 | TCP | Tenant UI | https://{external-ip} |
| 2443 | TCP | Deployment UI | https://{external-ip}:2443 |
| 3443 | TCP | Zitadel (auth) | https://{external-ip}:3443 |
| 4443 | TCP | Grafana | https://{external-ip}:4443 |
Admin Console
The Admin Console is always accessible on port 30000, regardless of DNS mode:
| Port | Protocol | Application | Description |
|---|---|---|---|
| 30000 | TCP | KOTS Admin Console | Installation management (https://{ip}:30000) |
Sensor Ports
These ports are used for sensor communication. Sensors send telemetry data to PCA and receive configuration updates:
| Port | Protocol | Service | Description |
|---|---|---|---|
| 443 | TCP | RoadRunner | Telemetry ingestion (gRPC over TLS) |
| 443 | TCP | Sensor-Orchestrator | Configuration distribution |
Inter-Node Communication
These ports must be open between all cluster nodes. They're used for Kubernetes control plane communication, etcd clustering, and pod networking:
| Port | Protocol | Component | Description |
|---|---|---|---|
| 2380 | TCP | etcd | etcd peer communication |
| 4789 | UDP | VXLAN | Pod network overlay |
| 6443 | TCP | Kubernetes API | API server |
| 9091 | TCP | kURL | kURL proxy |
| 9443 | TCP | kURL | kURL proxy (TLS) |
| 10250 | TCP | Kubelet | Kubelet API |
| 10249 | TCP | kube-proxy | Metrics |
| 10256 | TCP | kube-proxy | Health check |
Local Process Ports
These ports are used for local communication only and don't need to be opened in firewalls between nodes:
| Port | Protocol | Component | Description |
|---|---|---|---|
| 2379 | TCP | etcd | etcd client connections |
| 7443 | TCP | kURL | Registry proxy |
| 9099 | TCP | Calico | Felix health |
| 10248 | TCP | Kubelet | Health check |
| 10257 | TCP | kube-controller-manager | Secure port |
| 10259 | TCP | kube-scheduler | Secure port |
Internal Service Ports
These are the ports used by PCA services for internal communication. You generally don't need to configure these in external firewalls, but they're useful for troubleshooting:
| Service | Port | Health Endpoint | Expected Response |
|---|---|---|---|
| Gather | 80 | /health |
200 OK |
| Fedex | 80 | /health |
200 OK |
| Zitadel | 8080 | /healthz |
200 OK |
| Druid Coordinator | 8081 | /status |
200 OK |
| Health Clinic | 80 | /health |
200 OK |
Firewall Rule Examples
Use these examples as templates for configuring your firewall. Adjust IP addresses and CIDRs to match your environment.
iptables (Linux)
# External access (DNS mode)
iptables -A INPUT -p tcp --dport 443 -j ACCEPT
iptables -A INPUT -p tcp --dport 30000 -j ACCEPT

# Inter-node communication (replace with your node IPs)
NODE_IPS="<node-1-ip> <node-2-ip> <node-3-ip>"
for NODE_IP in $NODE_IPS; do
  iptables -A INPUT -s $NODE_IP -p tcp --dport 2380 -j ACCEPT
  iptables -A INPUT -s $NODE_IP -p udp --dport 4789 -j ACCEPT
  iptables -A INPUT -s $NODE_IP -p tcp --dport 6443 -j ACCEPT
  iptables -A INPUT -s $NODE_IP -p tcp --dport 10250 -j ACCEPT
done
firewalld (RHEL/CentOS)
# External access
firewall-cmd --permanent --add-port=443/tcp
firewall-cmd --permanent --add-port=30000/tcp

# Inter-node (create zone for cluster)
firewall-cmd --permanent --new-zone=pca-cluster
firewall-cmd --permanent --zone=pca-cluster --add-source=<node-cidr>
firewall-cmd --permanent --zone=pca-cluster --add-port=2380/tcp
firewall-cmd --permanent --zone=pca-cluster --add-port=4789/udp
firewall-cmd --permanent --zone=pca-cluster --add-port=6443/tcp
firewall-cmd --permanent --zone=pca-cluster --add-port=10250/tcp

firewall-cmd --reload
Cloud Security Groups (AWS/GCP/Azure)
Use these rules as a template for cloud security groups:
# Inbound Rules
Type        Protocol  Port    Source
HTTPS       TCP       443     0.0.0.0/0 (or restricted CIDR)
Custom TCP  TCP       30000   Admin IP range
Custom TCP  TCP       2380    Cluster security group (self)
Custom UDP  UDP       4789    Cluster security group (self)
Custom TCP  TCP       6443    Cluster security group (self)
Custom TCP  TCP       10250   Cluster security group (self)
Troubleshooting Network Issues
Use these commands when you suspect network connectivity problems.
Verify Port Connectivity
# From outside cluster
nc -zv <IP_ADDRESS> 443
nc -zv <IP_ADDRESS> 30000

# On a node to check listening ports
ss -tlnp | grep -E "(443|2443|3443|30000|6443)"

# Check inter-node connectivity
nc -zv <other-node-ip> 6443
nc -zv <other-node-ip> 2380
Common Issues
This table maps common symptoms to their likely network causes:
| Symptom | Check |
|---|---|
| Can't access UI | Port 443 open, DNS resolution, nginx pod running |
| Can't access Admin Console | Port 30000 open, kotsadm pod running |
| Nodes can't join cluster | Ports 6443, 2380, 10250 open between nodes |
| Pod networking issues | Port 4789/UDP open for VXLAN overlay |
© 2026 Cisco and/or its affiliates. All rights reserved.
For more information about trademarks, please visit: Cisco trademarks
For more information about legal terms, please visit: Cisco legal terms